If your business loses customer or employee information, or someone gets into it who shouldn’t, Alberta’s Personal Information Protection Act (PIPA) may require you to tell the Information and Privacy Commissioner. This guide covers PIPA breach reporting Alberta businesses need to know: when a report is mandatory, how to decide, what the report must contain, and what happens next.
The short answer: under section 34.1 of PIPA, you must notify the Commissioner “without unreasonable delay” when a reasonable person would consider that there is a real risk of significant harm to an individual. Not every incident meets that test, but every incident deserves a careful look and a written record. This article is general information, not legal advice. For a specific breach, speak with a privacy lawyer or contact the Office of the Information and Privacy Commissioner of Alberta (OIPC).
Key takeaways
- PIPA requires you to notify the Commissioner without unreasonable delay when a breach creates a real risk of significant harm (often shortened to RROSH) to someone.
- The OIPC recommends reporting as soon as possible, even if your internal investigation isn’t finished.
- Your written notice must cover eight items set out in section 19 of the PIPA Regulation, including your own assessment of the risk of harm.
- The Commissioner can require you to notify affected people directly. You can also notify them on your own first, and the OIPC encourages it when you believe the risk is real.
- Failing to notify the Commissioner is an offence. Organizations can be fined up to $100,000.
- As of October 2026, PIPA’s breach rules have not been replaced. Health custodians and public bodies follow different laws.
Who does PIPA apply to?
PIPA is Alberta’s private-sector privacy law. It applies to every organization and all personal information, with listed exceptions. In practice, that covers most Alberta businesses, for both customer and employee information.
Who follows different rules
- Health custodians. PIPA does not apply to health information covered by the Health Information Act (HIA). Clinics and other custodians have their own breach duties, which we cover in our cybersecurity checklist for Alberta clinics.
- Public bodies. On June 11, 2025, Alberta’s FOIP Act was repealed and replaced by the Access to Information Act and the Protection of Privacy Act (POPA). Municipalities, school divisions and other public bodies follow POPA, not PIPA.
- Non-profits. For non-profits that meet PIPA’s definition (for example, societies incorporated under the Societies Act), the OIPC explains that breach notification applies when the information was collected, used or disclosed in connection with a commercial activity.
Where federal law (PIPEDA) comes in
Alberta’s law has been deemed substantially similar to the federal Personal Information Protection and Electronic Documents Act (PIPEDA). But the Office of the Privacy Commissioner of Canada notes that federally regulated organizations are always subject to PIPEDA, such as banks, airlines and telecom companies. PIPEDA also applies to personal information crossing provincial or national borders in commercial activity. It has its own breach rules, including a requirement to keep records of all breaches of security safeguards for two years. If either applies, check both laws.
Has PIPA changed in 2025 or 2026?
Not the Alberta privacy breach notification rules. As of October 22, 2026, the official consolidation of PIPA on the Alberta King’s Printer site is current as of September 1, 2025, and sections 34.1 and 37.1 read as described in this article. The PIPA Regulation was last amended in 2026 and is current as of June 25, 2026. It now states an expiry date of June 30, 2028, and its breach notice sections (19 and 19.1) are unchanged.
A legislative committee began a review of PIPA on January 22, 2024, and the OIPC made a submission to that review on May 31, 2024. We found no bill in the Legislature’s 2025-2026 session to replace PIPA. Changes could still come, so check the King’s Printer site before relying on any summary, including this one.
What counts as a privacy breach under PIPA?
PIPA’s notice duty covers “any incident involving the loss of or unauthorized access to or disclosure of” personal information under your control. The OIPC’s guidance for notifying the Commissioner (April 2024) lists the incidents it commonly sees, including:
- Lost or stolen laptops, USB sticks and hard drives
- Emails, faxes or mail sent to the wrong person
- Staff “snooping” in customer records
- Hacking, malware and ransomware, including phishing attacks
- Insecure disposal of records, computers or storage media
Note the word “control.” If a contractor or software provider holding your data has the breach, the duty to notify usually stays with you, because you decide how the information is used.
The PIPA breach response flow, step by step
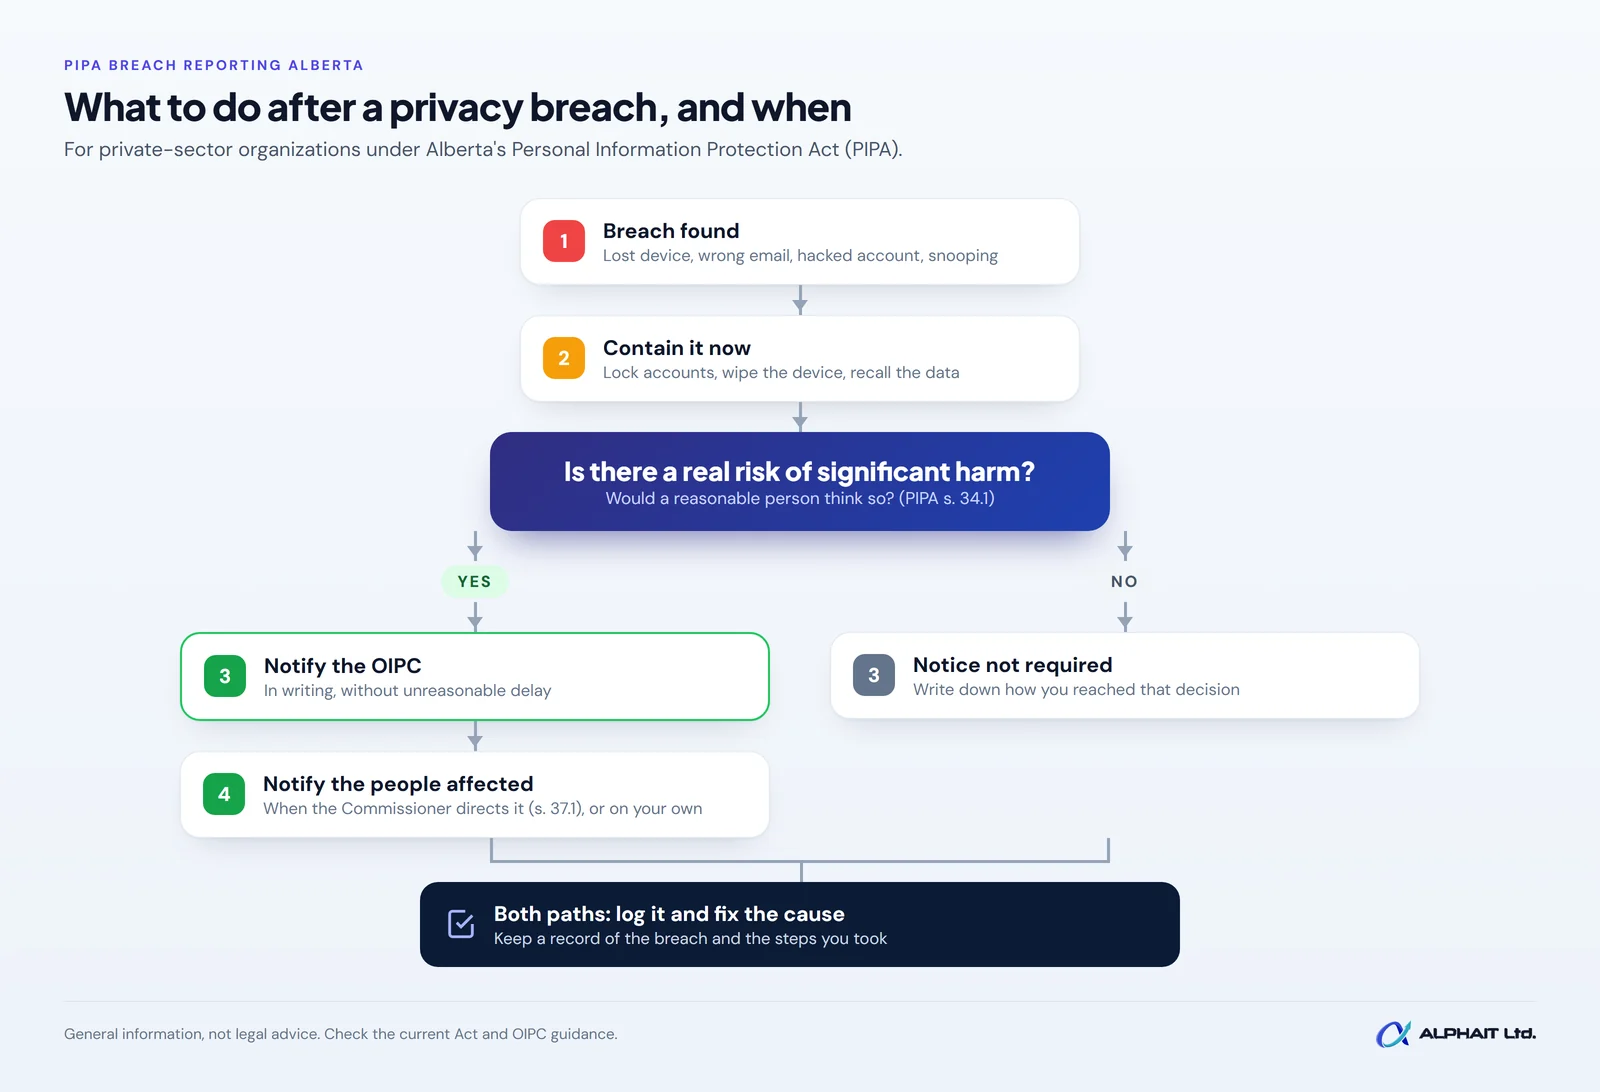
The OIPC’s Key Steps in Responding to Privacy Breaches sets out four steps: contain, evaluate the risks, notify and report, then prevent. It says the first three should happen right away, together or in quick succession.
1. Contain the breach
Stop the damage first: disable a compromised account, reset passwords, wipe a lost device remotely, ask a wrong recipient to delete an email, or take a system offline. Tell your privacy lead. The OIPC also suggests calling police if theft or other crime is involved.
2. Assess the risk, then notify
Decide whether there is a real risk of significant harm (explained below). If there is, notify the Commissioner without unreasonable delay and consider notifying affected people now rather than waiting to be told.
3. Document and prevent
Record what happened, what you decided and why. Then fix the cause. The OIPC suggests a security audit where needed, plus updated policies and training.
How to assess a real risk of significant harm in Alberta
The test has two parts, and both must be met.
Is the harm significant?
The OIPC describes significant harm as harm to the individual (not your business) that is “important, meaningful, and with non-trivial consequences.” Its guidance lists examples such as identity theft, fraud, financial loss, damage to a credit record, embarrassment or humiliation, damage to reputation or relationships, loss of employment or business opportunities, bodily harm, and blackmail or extortion.
Is the risk real?
According to the OIPC, the risk must be “more than mere speculation or conjecture,” with a cause and effect link between the breach and the harm. You have to consider all the circumstances. The OIPC’s factors are below, with the kind of answer that usually points to lower or higher risk.
| OIPC factor | Points to lower risk | Points to higher risk |
|---|---|---|
| What type of information is involved? | Names and business contact details only | SIN, driver’s licence, banking or credit card details, health or disciplinary information |
| Who got, or could get, access? | A known, trusted recipient who confirms deletion | Unknown people, a criminal, or the open internet |
| How many people saw it? | One person, by mistake | Many people, or posted publicly |
| Is there a relationship between the recipient and the person affected? | No connection | An ex-partner, family member or co-worker |
| Were safeguards like encryption in place? | Strong encryption, no known flaw | Unencrypted, or the password was exposed too |
| How long was it exposed? | Minutes, then removed | Weeks or months |
| Any sign of malicious intent? | Honest mistake | Theft, hacking, malware or ransomware |
| Could it be used for identity theft or fraud? | Not realistically | Yes |
| Was it recovered? | Fully recovered, not further shared | Not recovered |
| How many individuals are affected, and are any vulnerable? | Few adults | Many people, or youth or seniors involved |
The questions come from the OIPC guidance; the two right-hand columns are our illustrations, not OIPC rules. Weigh the factors together. The OIPC is clear that simply labelling a risk “low,” “medium” or “high” is not an assessment. To see how the Commissioner has ruled on real cases, browse its breach notification decisions or the 2022 PIPA Breach Report, which summarizes 10 years of them.
Quick decision table: what to do next
| Where you are | What to do |
|---|---|
| You suspect a breach | Contain it, preserve evidence such as logs, and start assessing right away |
| A reasonable person would see a real risk of significant harm | Notify the Commissioner without unreasonable delay, even if your investigation is still open |
| You believe the risk to individuals is real | Consider notifying them directly now, using the content required by Regulation section 19.1 |
| The Commissioner requires you to notify individuals | Do it in the form, manner and time frame the Commissioner sets |
| The test is not met | No notice to the Commissioner is required. Write down your reasoning and fix the cause |
| Federal law may apply (federally regulated, or data crossing borders) | Check PIPEDA’s reporting, notification and record-keeping rules as well |
How to report a privacy breach to the OIPC
The OIPC provides a PIPA Privacy Breach Notification Form. Its April 2024 guidance prefers email submission, with mail and fax as alternatives. Phoning the OIPC for general advice does not count as notifying the Commissioner: the notice must be in writing and meet the Regulation.
Section 19 of the PIPA Regulation says the notice must include:
- A description of what happened
- The date or time period of the breach
- A description of the personal information involved
- An assessment of the risk of harm to individuals
- An estimate of how many people face a real risk of significant harm
- Steps you’ve taken to reduce the risk of harm
- Steps you’ve taken to notify individuals
- The name and contact details of someone who can answer the Commissioner’s questions
Don’t wait until every box is filled. The OIPC recommends notifying as soon as possible, even before your investigation is complete. If there was a delay, the form asks you to explain it.
Do you have to notify affected individuals?
Under section 37.1, the Commissioner may require you to notify the people at risk, within a time period the Commissioner sets, and you must comply. Nothing stops you from notifying them yourself first, and the OIPC encourages organizations not to wait for direction when they believe there is a real risk.
When notice is required, section 19.1 of the Regulation says it must go directly to each person (unless the Commissioner decides direct notice would be unreasonable) and include:
- What happened
- When it happened
- What personal information was involved
- Steps you’ve taken to reduce the risk of harm
- Contact details for someone who can answer questions
Use this content even when you notify voluntarily. The OIPC’s advisory on notifying affected individuals warns that the Commissioner has required re-notification when an earlier notice fell short of the Regulation.
Keep a record of every breach
PIPA has no general rule requiring Alberta businesses to log every breach. We still recommend a simple breach log for every incident, including ones you don’t report: date found, what happened, information involved, your risk reasoning, who you notified and when, and what you changed.
A log shows the Commissioner, an insurer or a client that you took each incident seriously. If PIPEDA applies to you, record-keeping is a federal legal requirement.
What happens if you don’t report?
Failing to notify the Commissioner is an offence under section 59 of PIPA, with maximum fines of $10,000 for an individual and $100,000 for an organization. The Commissioner can also investigate whether you met the duty.
Reduce the chance of a reportable breach
Several OIPC risk factors, such as encryption and how long data was exposed, depend on your IT setup. Safeguards we recommend:
- Encrypt every laptop and phone that holds business data, and make sure you can wipe them remotely.
- Turn on multi-factor authentication everywhere.
- Limit access to customer and employee records to the people who need it.
- Remove access promptly when staff leave.
- Write a one-page breach plan naming who decides and who contacts the OIPC.
Our cybersecurity services for Edmonton businesses cover these controls, plus help with containing an incident and pulling together the technical facts your breach report needs.
Frequently asked questions
How long do I have to report a privacy breach in Alberta?
PIPA doesn’t set a number of days. It says “without unreasonable delay.” The OIPC recommends notifying as soon as possible once a real risk of significant harm exists, even before your investigation is finished.
Do I have to report a breach if no one has misused the data?
Possibly. The test is whether a reasonable person would see a real risk of significant harm, not whether harm has already happened. Weigh the OIPC factors, such as the type of information, who had access and whether it was encrypted or recovered.
Our IT provider or software vendor had the breach. Who reports it?
Usually you do, if the information is under your control. The OIPC guidance says a third party can notify on your behalf if you authorize it in writing.
Does a clinic report under PIPA?
Health information covered by the Health Information Act is excluded from PIPA, so health custodians follow HIA’s breach rules. If you’re unsure which law covers a record, ask the OIPC or a lawyer.
Related guides: Cybersecurity checklist for Alberta clinics, how to test backups, employee offboarding IT checklist, what to do in a ransomware attack.
Be ready before a breach happens
Plan your breach response before you need it. Take our free 3-minute IT check to see where gaps like unencrypted laptops or missing MFA could turn a small incident into a reportable one. To talk about cybersecurity for your Edmonton business, call the AlphaIT team at 780-318-0149.